Show summary Hide summary
- Why regulators are targeting AI now — and what that means
- New rules on the table and practical effects for companies
- How industry leaders and experts are responding
- Practical steps for developers, startups, and users
- Geography matters: how rules differ by region
- Short-term risks and long-term opportunities for innovation
- What to watch next — signals that rules are firming up
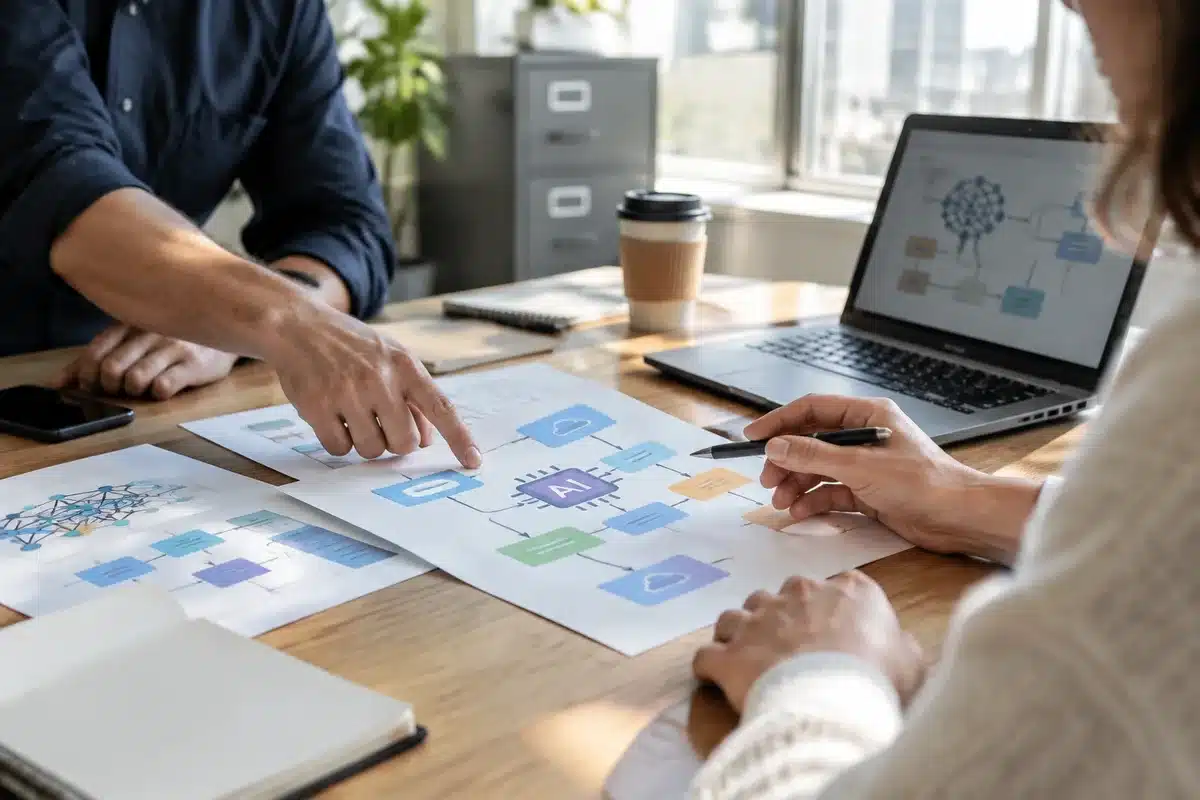
Governments around the world are intensifying efforts to regulate artificial intelligence, and the pace has surprised many in tech. New proposals and enforcement actions are reshaping how companies design products, train models, and share data. For users, the ripple effects could change privacy, the cost of services, and the pace of innovation.
Why regulators are targeting AI now — and what that means
Lawmakers cite risks from biased algorithms, deepfakes, and opaque decision-making. Public pressure is rising after several high-profile incidents. At the same time, AI systems are moving into critical domains like healthcare and finance.
Jet-powered Harley rockets to 60 mph on pure thrust: twin diesel jets, no drivetrain
Expensive gasoline pushing drivers to electric vehicles: will you switch?
- Risk amplification: AI can scale harm quickly when errors are embedded.
- Opacity problem: Many models lack clear explanations for their outputs.
- Market reach: AI tools are now embedded in services used by millions.
Common policy goals among regulators
Despite different approaches, regulators pursue similar outcomes.
- Increase transparency in how models are trained and tested.
- Force accountability for harms and discrimination.
- Set safety standards for high-risk AI applications.
New rules on the table and practical effects for companies
Draft rules range from disclosure requirements to strict audits for certain systems. Firms may need to redesign workflows and invest in compliance staff.
Key compliance demands businesses will face
- Documentation of training data and evaluation methods.
- Independent third-party audits for systems deemed high risk.
- Human oversight standards where automated choices affect rights.
- Data residency and protection rules affecting model hosting.
Costs, timelines, and operational changes
Smaller players may feel the burden faster than large tech firms. Compliance can require new tooling, legal reviews, and longer release cycles.
- Initial assessment and gap analysis: weeks to months.
- Audit and mitigation: months depending on complexity.
- Ongoing monitoring and reporting: continuous effort.
How industry leaders and experts are responding
Executives promise adaptation, while advocacy groups call for stronger limits. Researchers warn that rules written without technical input may backfire.
Corporate strategies
- Some firms preemptively disclose model details to build trust.
- Others argue for flexible, risk-based frameworks to preserve innovation.
- Partnerships are forming between tech companies and compliance vendors.
Voices from civil society and academia
- Privacy groups demand clearer rights for affected users.
- Researchers urge standards for benchmark testing and reproducibility.
- Legal scholars emphasize enforceable remedies for harms.
Practical steps for developers, startups, and users
Preparation now will cut costs and headaches later. A measured approach can protect users and preserve product value.
- Perform a risk assessment to classify systems by impact level.
- Document data provenance and preprocessing steps.
- Implement explainability tools where decisions affect people.
- Set up incident response plans for model failures or misuse.
- Engage legal counsel early to track evolving rules.
Tools and resources worth considering
- Open standards for model cards and data sheets.
- Automated testing suites for bias and robustness checks.
- Privacy-preserving techniques like differential privacy.
Geography matters: how rules differ by region
Regulatory tone and strictness vary by jurisdiction. Companies need a multi-jurisdiction strategy when they operate globally.
- Some regions favor strict, precautionary rules for all AI products.
- Others opt for sector-specific guidance focused on high-risk uses.
- Cross-border data flow restrictions can affect cloud deployments.
Questions to map jurisdictional risk
- Where will models be trained and hosted?
- Which markets classify the product as high risk?
- Are there data localization or consent rules in target countries?
Short-term risks and long-term opportunities for innovation
Tighter rules create short-term friction. They also spur investment in safer AI design and trustworthy practices.
- Risk: Increased compliance costs can slow startups.
- Opportunity: Demand grows for tools that provide auditability.
- Market shift: Services that prove safety may win customer trust.
Business models that could thrive
- SaaS platforms offering compliance as a service.
- Consultancies specializing in model audits and documentation.
- Open-source projects that standardize safety checks.
What to watch next — signals that rules are firming up
Track legislative calendars, regulator guidance, and major enforcement actions. Industry standards and court decisions will also shape outcomes.
- Publication of final rulebooks by national regulators.
- High-profile fines or mandates against large providers.
- Adoption of industry consensus standards and testing suites.
Stakeholders across tech, law, and civil society are now negotiating how to balance safety, rights, and innovation. The next months will set precedents that could last years.